SaaS Ranking

Vast.ai: what they publish

vast.ai · MLOps and model serving · checked 2026-10-20

52/100DBand D

Rank 5 of 35 in MLOps and model serving, where the median is 22.

Public transparency score, not a product or security rating. Latest check: 2026-10-20. How the score works.

Evidence at a glance

Choose a check to see its source, date and scope.

Not found means not found at the addresses we checked. Not measured means we could not complete the check.

Start a vendor reviewDownload evidence (CSV)

Overview

0 days since the newest dated result, 0 since the oldest. 12 of 12 criteria have a measured result in the last 30 days. Failed checks and undated results are excluded.

Evidence freshness is a statement about our measurement and is kept apart from the transparency score, which is frozen at v1. How good our own measurement is.

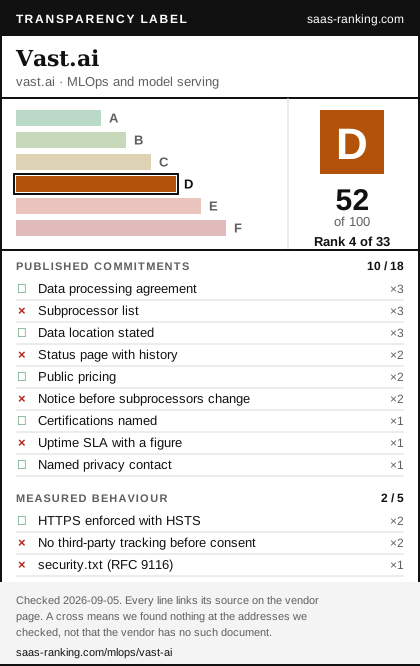
Transparency labelsaas-ranking.com

Vast.ai

vast.ai · MLOps and model serving

  1. A
  2. B
  3. C
  4. D
  5. E
  6. F
D 52of 100 Rank 5 of 35

Published commitments5 of 9 found

Measured behaviour1 of 3 found

Checked 2026-10-20. Every line links the page we found it on. A cross means we found nothing at the addresses we checked, not that the vendor has no such document. A transparency score, not a product rating.

Downloads include all checks, source URLs, dates and the snapshot ID for your procurement file. We do not issue badges.

The label is the whole measurement in one object: every criterion with its weight, the band, and the date. Public transparency score, not a product or security rating.

Every line in it links the page we found the result on, or lists the addresses we checked. A cross means we found nothing there, not that Vast.ai has no such document.

Where Vast.ai sits in MLOps and model serving

  1. A0 0%
  2. B0 0%
  3. C1 3%
  4. D6 17%
  5. E10 29%
  6. F18 51%
35 vendors with a score; 2 more without a score because we could measure too little. Bands have fixed thresholds, see how the score works.

The band of Vast.ai is marked. Vendors without a score are the ones where we could measure too few criteria to rank them – a gap on our side, counted separately.

What Vast.ai states

The exact figures and names we read off the pages linked below, with the sentence they stand in. This is what they publish, not what we verified about their systems.

Gaps, heaviest first

✗

Subprocessors: the published list

weight 3 of 3

No subprocessor list found.

Checked 7 addresses on 2026-10-20.

Show the 7 addresses we checked
  1. https://vast.ai/legal/subprocessors – reached, no match (HTTP 404)
  2. https://vast.ai/subprocessors – reached, no match (HTTP 404)
  3. https://vast.ai/sub-processors – reached, no match (HTTP 404)
  4. https://vast.ai/legal/sub-processors – reached, no match (HTTP 404)
  5. https://vast.ai/trust/subprocessors – reached, no match (HTTP 404)
  6. https://vast.ai/privacy/subprocessors – reached, no match (HTTP 404)
  7. https://vast.ai/legal/subprocessor-list – reached, no match (HTTP 404)

Is this wrong? Send us the URL

Across the market: Subprocessor list in MLOps and model serving: 2 of 35 companies

✗

Status page with incident history

weight 2 of 3

No public status page found.

Checked 3 addresses on 2026-10-20.

Show the 3 addresses we checked
  1. https://status.vast.ai/ – reached, no match (HTTP 200)
  2. https://vast.ai/status – reached, no match (HTTP 200)
  3. https://vast.ai.statuspage.io/ – Could not be fetched: fetch failed.

Is this wrong? Send us the URL

Across the market: Status page with history in MLOps and model serving: 12 of 37 companies

✗weight 2 of 3

Third-party requests seen on the first load, before any interaction.

Checked 1 address on 2026-10-20.

Show the 1 address we checked
  1. https://vast.ai/ – third-party requests before any interaction: app.posthog.com, cmp.osano.com, growthbook-cwfl3phrgq-uc.a.run.app, storage.googleapis.com, www.googletagmanager.com

Is this wrong? Send us the URL

Across the market: No third-party tracking before consent in MLOps and model serving: 1 of 37 companies

✗

Notice before subprocessors change

weight 2 of 3

No commitment to give notice before subprocessors change found.

Checked 8 addresses on 2026-10-20.

Show the 8 addresses we checked
  1. https://vast.ai/legal/subprocessors – reached, no match (HTTP 404)
  2. https://vast.ai/subprocessors – reached, no match (HTTP 404)
  3. https://vast.ai/sub-processors – reached, no match (HTTP 404)
  4. https://vast.ai/legal/dpa – reached, no match (HTTP 404)
  5. https://vast.ai/dpa – reached, no match (HTTP 404)
  6. https://vast.ai/legal/data-processing-agreement – reached, no match (HTTP 404)
  7. https://vast.ai/trust/subprocessors – reached, no match (HTTP 404)
  8. https://vast.ai/legal/sub-processors – reached, no match (HTTP 404)

Is this wrong? Send us the URL

Across the market: Notice before subprocessors change in MLOps and model serving: 5 of 35 companies

✗

Uptime SLA with a figure

weight 1 of 3

No uptime figure found.

Checked 6 addresses on 2026-10-20.

Show the 6 addresses we checked
  1. https://vast.ai/legal/sla – reached, no match (HTTP 404)
  2. https://vast.ai/sla – reached, no match (HTTP 404)
  3. https://vast.ai/legal/service-level-agreement – reached, no match (HTTP 404)
  4. https://vast.ai/trust/sla – reached, no match (HTTP 404)
  5. https://vast.ai/uptime – reached, no match (HTTP 404)
  6. https://vast.ai/legal/uptime-sla – reached, no match (HTTP 404)

Is this wrong? Send us the URL

Across the market: Uptime SLA with a figure in MLOps and model serving: 1 of 35 companies

✗

security.txt (RFC 9116)

weight 1 of 3

No security.txt found.

Checked 1 address on 2026-10-20.

Show the 1 address we checked
  1. https://vast.ai/.well-known/security.txt – reached, no match (HTTP 404)

Is this wrong? Send us the URL

Across the market: security.txt (RFC 9116) in MLOps and model serving: 11 of 34 companies

Evidence

The full source lists sit behind these two groups, so that the answer above stays readable.

Published, with a source 6
✓

Data processing agreement (DPA)

weight 3 of 3

Published and readable without a login.

Source: https://vast.ai/data-processing-agreement · checked 2026-10-20

Across the market: Data processing agreement in MLOps and model serving: 6 of 35 companies

✓

Data location: where they say data is hosted

weight 3 of 3

The hosting location is stated on a public page.

  • Locations named next to the hosting wording United States. This does not establish the company’s headquarters.
    Show the exact wording

    The Website is hosted in the United States of America and is subject to U.S.

    Read at https://vast.ai/privacy

Source: https://vast.ai/privacy · checked 2026-10-20

Across the market: Data location stated in MLOps and model serving: 9 of 36 companies

✓

Public pricing with figures

weight 2 of 3

Actual numbers on a public page.

Source: https://vast.ai/pricing · checked 2026-10-20

Across the market: Public pricing in MLOps and model serving: 19 of 36 companies

✓

HTTPS enforced with HSTS

weight 2 of 3

HTTP redirects to HTTPS and the HSTS header is set.

  • HSTS max-age 63072000 seconds (730 days).
    Show the exact wording

    max-age=63072000

    Read at https://vast.ai/

Source: https://vast.ai/ · checked 2026-10-20

Across the market: HTTPS enforced with HSTS in MLOps and model serving: 28 of 37 companies

✓

Certifications named (SOC 2, ISO 27001)

weight 1 of 3

SOC 2 or ISO 27001 named on a public page.

  • Named on that page HIPAA (not counted: the sentence does not carry it), HITRUST CSF (not counted: the sentence does not carry it), ISO 22301 (not counted: the sentence does not carry it), ISO/IEC 27001 (not counted: the sentence does not carry it), PCI DSS (not counted: the sentence does not carry it), SOC 2 Type II. The sentence we kept does not carry this finding on its own, so it counts in no list and no figure.
    Show the 6 exact wordings

    HIPAA Vast.ai supports HIPAA-covered workloads on our Secure Cloud tier.

    Read at https://vast.ai/compliance

    may include: ISO 27001, ISO 20000-1, ISO 22301, ISO 14001 SOC 1 Type 2, SOC 2 Type 2, SOC 3 HIPAA, HITRUST, PCI DSS NIST frameworks Security certifications such as ISO 27001 or SOC 2 are encouraged an...

    Read at https://vast.ai/compliance

    d business identity Certifications held by datacenter partners may include: ISO 27001, ISO 20000-1, ISO 22301, ISO 14001 SOC 1 Type 2, SOC 2 Type 2, SOC 3 HIPAA, HITRUST, PCI DSS NIST frameworks Secur...

    Read at https://vast.ai/compliance

    security, ownership, and business identity Certifications held by datacenter partners may include: ISO 27001, ISO 20000-1, ISO 22301, ISO 14001 SOC 1 Type 2, SOC 2 Type 2, SOC 3 HIPAA, HITRUST, PCI DS...

    Read at https://vast.ai/compliance

    ude: ISO 27001, ISO 20000-1, ISO 22301, ISO 14001 SOC 1 Type 2, SOC 2 Type 2, SOC 3 HIPAA, HITRUST, PCI DSS NIST frameworks Security certifications such as ISO 27001 or SOC 2 are encouraged and streng...

    Read at https://vast.ai/compliance

    SOC 2 Type 2 Vast.ai has completed SOC 2 Type 2 certification.

    Read at https://vast.ai/compliance

Source: https://vast.ai/compliance · checked 2026-10-20

Across the market: Certifications named in MLOps and model serving: 13 of 36 companies

✓

Named privacy contact (DPO or privacy address)

weight 1 of 3

A data protection officer or a dedicated privacy address is named.

  • What the privacy page carries Named data protection officer.
    Show the exact wording

    Data Protection Officer

    Read at https://vast.ai/privacy

Source: https://vast.ai/privacy · checked 2026-10-20

Across the market: Named privacy contact in MLOps and model serving: 15 of 36 companies

History

100 0 2026-10-13: 52 of 1002026-10-20: 52 of 100 2026-10-13 2026-10-20
Score over the last 2 runs we measured Vast.ai in: 52 (2026-10-13), 52 (2026-10-20).

Prepare your vendor review

A source is a starting point. Check the product, plan, legal entity and date before treating it as evidence for your purchase. These questions do not change the transparency score.

Vast.ai

6 found · 6 not found · 0 not measured across 12 public checks.

12 of 12 criteria have a measured result from the last 30 days. Oldest dated result: 2026-10-20.

Investigate 6 open evidence questions
  1. Subprocessor list

    Which subprocessors apply to our product, what does each process, and in which countries? Please share the current list.

    Inspect this check
  2. Status page with history

    Where can we review incident history for the service we will use, and how do we subscribe to incident updates?

    Inspect this check
  3. Uptime SLA with a figure

    Which availability commitment applies to our plan? Please include the measurement window, exclusions and credit claim process.

    Inspect this check
  4. No third-party tracking before consent

    Which third-party requests occur before a visitor makes a choice, and for what purpose? Please distinguish the public website from the product.

    Inspect this check
  5. security.txt (RFC 9116)

    Where should we report a vulnerability, and what acknowledgement and follow-up process should we expect?

    Inspect this check
  6. Notice before subprocessors change

    How will you notify us before a subprocessor changes, with how much notice, and what response options apply to our contract?

    Inspect this check

Compare

A shortlist holds up to six vendors across categories and lives entirely in the address of its page: share the link, bookmark it, put it in a ticket. Nothing is stored, so we do not know it exists.