✓
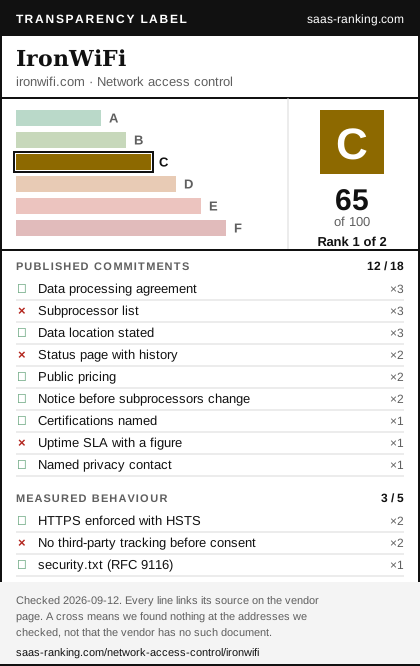
Data processing agreement (DPA)
weight 3 of 3
Published and readable without a login.
Source: https://www.ironwifi.com/dpa · checked 2026-10-28
✓
Data location: where they say data is hosted
weight 3 of 3
The hosting location is stated on a public page.
- Locations named next to the hosting wording United States. This does not establish the company’s headquarters.
Show the exact wording
s are stored by our cloud provider, Google, in a global storage location (which may be in any region) and in a log archive in the United States; transfers are covered by the safeguards in Google's dat
Read at https://www.ironwifi.com/privacy-policy
Source: https://www.ironwifi.com/privacy-policy · checked 2026-10-28
✓
HTTPS enforced with HSTS
weight 2 of 3
HTTP redirects to HTTPS and the HSTS header is set.
- HSTS max-age 15552000 seconds (180 days).
Show the exact wording
max-age=15552000; includeSubDomains; preload
Read at https://ironwifi.com/
- HSTS options includeSubDomains, preload.
Show the 2 exact wordings
max-age=15552000; includeSubDomains; preload
Read at https://ironwifi.com/
max-age=15552000; includeSubDomains; preload
Read at https://ironwifi.com/
Source: https://ironwifi.com/ · checked 2026-10-28
✓
Notice before subprocessors change
weight 2 of 3
The vendor commits publicly to giving notice before the list changes.
Source: https://www.ironwifi.com/dpa · checked 2026-10-28
✓
Certifications named (SOC 2, ISO 27001)
weight 1 of 3
SOC 2 or ISO 27001 named on a public page.
- Named on that page FedRAMP (not counted: the sentence does not carry it), HIPAA (not counted: the sentence does not carry it), ISO/IEC 27001 (not counted: the sentence does not carry it), PCI DSS (not counted: the sentence does not carry it), SOC 2 Type II. The sentence we kept does not carry this finding on its own, so it counts in no list and no figure.
Show the 5 exact wordings
See the control mapping FedRAMP Marketplace Listed under FedRAMP ID FR2631154499, Initial Implementation Phase since 12 August 2026
Read at https://www.ironwifi.com/compliance/
ard secrecy Agreements for Regulated Industries Whether you need a Business Associate Agreement for HIPAA or a Data Processing Agreement for GDPR, we've got you covered.
Read at https://www.ironwifi.com/compliance/
ISO 27001 Aligned Information security management practices aligned with ISO 27001 standards.
Read at https://www.ironwifi.com/compliance/
ecialist IronWiFi is SOC 2 Type II attested and supports compliance with HIPAA, GDPR, NIS2, and PCI DSS through TLS 1.3 encryption, complete audit logging of all authentication events, and data reside
Read at https://www.ironwifi.com/compliance/
tifications & Standards Built to meet the security requirements of the most regulated industries SOC 2 Type II Our infrastructure and processes are audited annually against Trust Service Criteria for
Read at https://www.ironwifi.com/compliance/
Source: https://www.ironwifi.com/compliance/ · checked 2026-10-28