SaaS Ranking

Dataminr: what they publish

dataminr.com · Threat intelligence · checked 2026-10-14

70/100BBand B

Rank 1 of 35 in Threat intelligence, where the median is 17.

Public transparency score, not a product or security rating. Latest check: 2026-10-14. How the score works.

Evidence at a glance

Choose a check to see its source, date and scope.

Not found means not found at the addresses we checked. Not measured means we could not complete the check.

Start a vendor reviewDownload evidence (CSV)

Overview

4 days since the newest dated result, 4 since the oldest. 12 of 12 criteria have a measured result in the last 30 days. Failed checks and undated results are excluded.

Evidence freshness is a statement about our measurement and is kept apart from the transparency score, which is frozen at v1. How good our own measurement is.

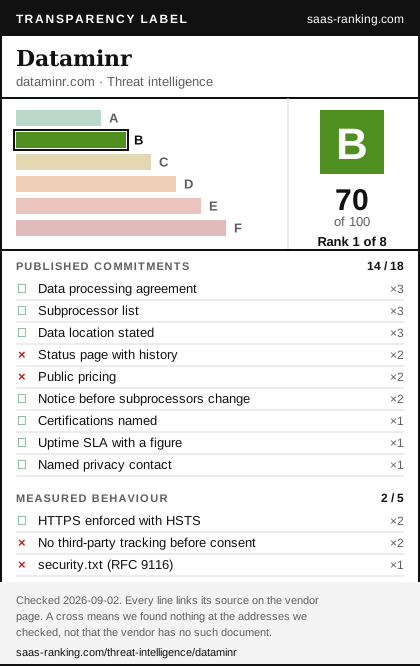
Transparency labelsaas-ranking.com

Dataminr

dataminr.com · Threat intelligence

  1. A
  2. B
  3. C
  4. D
  5. E
  6. F
B 70of 100 Rank 1 of 35

Published commitments7 of 9 found

Measured behaviour1 of 3 found

Checked 2026-10-14. Every line links the page we found it on. A cross means we found nothing at the addresses we checked, not that the vendor has no such document. A transparency score, not a product rating.

Downloads include all checks, source URLs, dates and the snapshot ID for your procurement file. We do not issue badges.

The label is the whole measurement in one object: every criterion with its weight, the band, and the date. Public transparency score, not a product or security rating.

Every line in it links the page we found the result on, or lists the addresses we checked. A cross means we found nothing there, not that Dataminr has no such document.

Where Dataminr sits in Threat intelligence

  1. A0 0%
  2. B1 3%
  3. C0 0%
  4. D3 9%
  5. E9 26%
  6. F22 63%
35 vendors with a score; 3 more without a score because we could measure too little. Bands have fixed thresholds, see how the score works.

The band of Dataminr is marked. Vendors without a score are the ones where we could measure too few criteria to rank them – a gap on our side, counted separately.

What Dataminr states

The exact figures and names we read off the pages linked below, with the sentence they stand in. This is what they publish, not what we verified about their systems.

Gaps, heaviest first

✗

Status page with incident history

weight 2 of 3

We found this behind a sign-in, so it is not published openly.

Seen at https://status.dataminr.com/access/login · checked 2026-10-14

Show the 3 addresses we checked
  1. https://status.dataminr.com/ – found, but behind a sign-in
  2. https://dataminr.com/status – reached, no match (HTTP 404)
  3. https://dataminr.com.statuspage.io/ – Could not be fetched: fetch failed.

Is this wrong? Send us the URL

Across the market: Status page with history in Threat intelligence: 5 of 36 companies

✗

Public pricing with figures

weight 2 of 3

No public pricing with figures found.

Checked 5 addresses on 2026-10-14.

Show the 5 addresses we checked
  1. https://dataminr.com/pricing – reached, no match (HTTP 404)
  2. https://dataminr.com/pricing/ – reached, no match (HTTP 404)
  3. https://dataminr.com/plans – reached, no match (HTTP 404)
  4. https://dataminr.com/en/pricing – reached, no match (HTTP 404)
  5. https://dataminr.com/pricing-plans – reached, no match (HTTP 404)

Is this wrong? Send us the URL

Across the market: Public pricing in Threat intelligence: 6 of 35 companies

✗weight 2 of 3

Third-party requests seen on the first load, before any interaction.

Checked 1 address on 2026-10-14.

Show the 1 address we checked
  1. https://dataminr.com/ – third-party requests before any interaction: a.usbrowserspeed.com, app.qualified.com, bat.bing.com, bat.bing.net, cdn.cookielaw.org, cdn.jsdelivr.net, geolocation.onetrust.com, js.qualified.com, pagead2.googlesyndication.com, region1.google-analytics.com, tracking.intentsify.io, www.googletagmanager.com

Is this wrong? Send us the URL

Across the market: No third-party tracking before consent in Threat intelligence: 4 of 38 companies

✗

security.txt (RFC 9116)

weight 1 of 3

No security.txt found.

Checked 1 address on 2026-10-14.

Show the 1 address we checked
  1. https://dataminr.com/.well-known/security.txt – reached, no match (HTTP 404)

Is this wrong? Send us the URL

Across the market: security.txt (RFC 9116) in Threat intelligence: 5 of 36 companies

Evidence

The full source lists sit behind these two groups, so that the answer above stays readable.

Published, with a source 8
✓

Data processing agreement (DPA)

weight 3 of 3

Published and readable without a login.

Source: https://www.dataminr.com/legal/dpa/ · checked 2026-10-14

Across the market: Data processing agreement in Threat intelligence: 5 of 36 companies

✓

Subprocessors: the published list

weight 3 of 3

The actual list is published, not just a promise to keep one.

Source: https://www.dataminr.com/legal/sub-processors/ · checked 2026-10-14

Across the market: Subprocessor list in Threat intelligence: 3 of 36 companies

✓

Data location: where they say data is hosted

weight 3 of 3

The hosting location is stated on a public page.

Source: https://www.dataminr.com/v1/dataminr-trust-services/ · checked 2026-10-14

Across the market: Data location stated in Threat intelligence: 11 of 36 companies

✓

HTTPS enforced with HSTS

weight 2 of 3

HTTP redirects to HTTPS and the HSTS header is set.

  • HSTS max-age 31536000 seconds (365 days).
    Show the exact wording

    max-age=31536000; includeSubDomains

    Read at https://dataminr.com/
  • HSTS options includeSubDomains.
    Show the exact wording

    max-age=31536000; includeSubDomains

    Read at https://dataminr.com/

Source: https://dataminr.com/ · checked 2026-10-14

Across the market: HTTPS enforced with HSTS in Threat intelligence: 25 of 37 companies

✓

Notice before subprocessors change

weight 2 of 3

The vendor commits publicly to giving notice before the list changes.

Source: https://www.dataminr.com/legal/dpa/ · checked 2026-10-14

Across the market: Notice before subprocessors change in Threat intelligence: 4 of 35 companies

✓

Certifications named (SOC 2, ISO 27001)

weight 1 of 3

SOC 2 or ISO 27001 named on a public page.

  • Named on that page Cyber Essentials, ISO/IEC 27001 (not counted: the sentence does not carry it), ISO/IEC 27701, SOC 2 Type II (not counted: the sentence does not carry it). The sentence we kept does not carry this finding on its own, so it counts in no list and no figure.
    Show the 4 exact wordings

    d compliance Dataminr is SOC 2 Type 2, NIST 800-171, ISO/IEC 27001:2013, ISO/IEC 27701:2019, and UK Cyber Essentials Plus certified.

    Read at https://www.dataminr.com/v1/dataminr-trust-services/

    Third-party verification and compliance Dataminr is SOC 2 Type 2, NIST 800-171, ISO/IEC 27001:2013, ISO/IEC 27701:2019, and UK Cyber Essentials Plus certified.

    Read at https://www.dataminr.com/v1/dataminr-trust-services/

    Third-party verification and compliance Dataminr is SOC 2 Type 2, NIST 800-171, ISO/IEC 27001:2013, ISO/IEC 27701:2019, and UK Cyber Essentials Plus certified.

    Read at https://www.dataminr.com/v1/dataminr-trust-services/

    Third-party verification and compliance Dataminr is SOC 2 Type 2, NIST 800-171, ISO/IEC 27001:2013, ISO/IEC 27701:2019, and UK Cyber Essentials Plus certifie

    Read at https://www.dataminr.com/v1/dataminr-trust-services/

Source: https://www.dataminr.com/v1/dataminr-trust-services/ · checked 2026-10-14

Across the market: Certifications named in Threat intelligence: 7 of 37 companies

✓

Uptime SLA with a figure

weight 1 of 3

An availability commitment with a figure.

  • Highest uptime figure on that page 99 %.
    Show the exact wording

    Service Level Guarantee Dataminr will make the Services available 99% of the time on a monthly basis.

    Read at https://www.dataminr.com/legal/sla/

Source: https://www.dataminr.com/legal/sla/ · checked 2026-10-14

Across the market: Uptime SLA with a figure in Threat intelligence: 3 of 35 companies

✓

Named privacy contact (DPO or privacy address)

weight 1 of 3

A data protection officer or a dedicated privacy address is named.

Source: https://www.dataminr.com/privacy-policy/ · checked 2026-10-14

Across the market: Named privacy contact in Threat intelligence: 12 of 36 companies

History

100 0 2026-10-07: 70 of 1002026-10-14: 70 of 100 2026-10-07 2026-10-14
Score over the last 2 runs we measured Dataminr in: 70 (2026-10-07), 70 (2026-10-14).

Prepare your vendor review

A source is a starting point. Check the product, plan, legal entity and date before treating it as evidence for your purchase. These questions do not change the transparency score.

Dataminr

8 found · 4 not found · 0 not measured across 12 public checks.

12 of 12 criteria have a measured result from the last 30 days. Oldest dated result: 2026-10-14.

Investigate 4 open evidence questions
  1. Status page with history

    Where can we review incident history for the service we will use, and how do we subscribe to incident updates?

    Inspect this check
  2. Public pricing

    Please confirm the total cost for our seats and usage, including minimum commitments, add-ons, overages and renewal terms.

    Inspect this check
  3. No third-party tracking before consent

    Which third-party requests occur before a visitor makes a choice, and for what purpose? Please distinguish the public website from the product.

    Inspect this check
  4. security.txt (RFC 9116)

    Where should we report a vulnerability, and what acknowledgement and follow-up process should we expect?

    Inspect this check

Compare

A shortlist holds up to six vendors across categories and lives entirely in the address of its page: share the link, bookmark it, put it in a ticket. Nothing is stored, so we do not know it exists.