✗
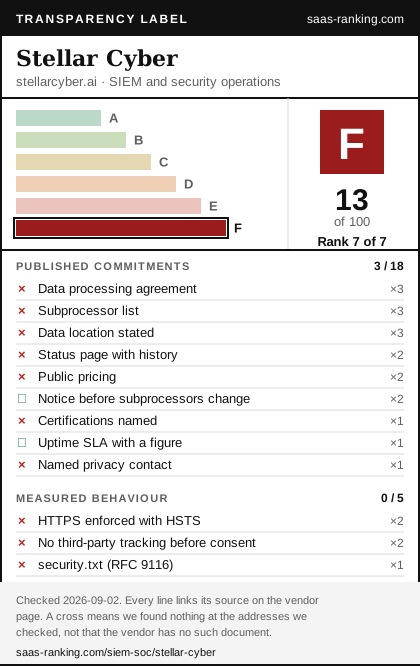
Data processing agreement (DPA)
weight 3 of 3
No data processing agreement found.
Checked 8 addresses on 2026-10-14.
Show the 8 addresses we checked
https://stellarcyber.ai/legal/dpa – reached, no match (HTTP 200)https://stellarcyber.ai/dpa – reached, no match (HTTP 200)https://stellarcyber.ai/legal/data-processing-agreement – reached, no match (HTTP 200)https://stellarcyber.ai/data-processing-agreement – reached, no match (HTTP 200)https://stellarcyber.ai/legal/data-processing-addendum – reached, no match (HTTP 200)https://stellarcyber.ai/legal/gdpr – reached, no match (HTTP 200)https://stellarcyber.ai/trust/dpa – reached, no match (HTTP 200)https://stellarcyber.ai/privacy/dpa – reached, no match (HTTP 200)
Is this wrong? Send us the URL
Across the market: Data processing agreement in SIEM and security operations: 8 of 39 companies
✗
Subprocessors: the published list
weight 3 of 3
No subprocessor list found.
Checked 7 addresses on 2026-10-14.
Show the 7 addresses we checked
https://stellarcyber.ai/legal/subprocessors – reached, no match (HTTP 200)https://stellarcyber.ai/subprocessors – reached, no match (HTTP 200)https://stellarcyber.ai/sub-processors – reached, no match (HTTP 200)https://stellarcyber.ai/legal/sub-processors – reached, no match (HTTP 200)https://stellarcyber.ai/trust/subprocessors – reached, no match (HTTP 200)https://stellarcyber.ai/privacy/subprocessors – reached, no match (HTTP 200)https://stellarcyber.ai/legal/subprocessor-list – reached, no match (HTTP 200)
Is this wrong? Send us the URL
Across the market: Subprocessor list in SIEM and security operations: 3 of 39 companies
✗
Data location: where they say data is hosted
weight 3 of 3
No statement about data location found.
Checked 7 addresses on 2026-10-14.
Show the 7 addresses we checked
https://stellarcyber.ai/security – Not the expected content type but "image/svg+xml".https://stellarcyber.ai/trust – reached, no match (HTTP 200)https://stellarcyber.ai/legal/privacy – reached, no match (HTTP 200)https://stellarcyber.ai/privacy – reached, no match (HTTP 200)https://stellarcyber.ai/privacy-policy – reached, no match (HTTP 200)https://stellarcyber.ai/compliance – reached, no match (HTTP 200)https://stellarcyber.ai/legal/privacy-policy – reached, no match (HTTP 200)
Is this wrong? Send us the URL
Across the market: Data location stated in SIEM and security operations: 8 of 39 companies
✗
Public pricing with figures
weight 2 of 3
No public pricing with figures found.
Checked 5 addresses on 2026-10-14.
Show the 5 addresses we checked
https://stellarcyber.ai/pricing – reached and rendered, no matchhttps://stellarcyber.ai/pricing/ – reached, no match (HTTP 200)https://stellarcyber.ai/plans – reached, no match (HTTP 200)https://stellarcyber.ai/en/pricing – reached, no match (HTTP 200)https://stellarcyber.ai/pricing-plans – reached, no match (HTTP 200)
Is this wrong? Send us the URL
Across the market: Public pricing in SIEM and security operations: 8 of 40 companies
✗
No third-party tracking before consent
weight 2 of 3
Third-party requests seen on the first load, before any interaction.
- Third-party hosts we saw on the first load 23 arttrk.com, bing.com, bing.net, bizible.com, bizibly.com, clarity.ms, doubleclick.net, google.com, google.de, googletagmanager.com, hs-analytics.net, hs-banner.com, hubspot.com, licdn.com, linkedin.com, marketo.net, mktoresp.com, navattic.com, reddit.com, redditstatic.com, techtarget.com, usemessages.com, zi-scripts.com.
Show the 23 exact wordings
arttrk.com
Read at https://stellarcyber.ai/
bat.bing.com
Read at https://stellarcyber.ai/
bat.bing.net
Read at https://stellarcyber.ai/
cdn.bizible.com
Read at https://stellarcyber.ai/
cdn.bizibly.com
Read at https://stellarcyber.ai/
o.clarity.ms, scripts.clarity.ms, www.clarity.ms
Read at https://stellarcyber.ai/
ad.doubleclick.net, stats.g.doubleclick.net
Read at https://stellarcyber.ai/
region1.analytics.google.com, www.google.com
Read at https://stellarcyber.ai/
www.google.de
Read at https://stellarcyber.ai/
www.googletagmanager.com
Read at https://stellarcyber.ai/
js.hs-analytics.net
Read at https://stellarcyber.ai/
js.hs-banner.com
Read at https://stellarcyber.ai/
api.hubspot.com, track.hubspot.com
Read at https://stellarcyber.ai/
snap.licdn.com
Read at https://stellarcyber.ai/
px.ads.linkedin.com
Read at https://stellarcyber.ai/
munchkin.marketo.net
Read at https://stellarcyber.ai/
828-dzv-249.mktoresp.com
Read at https://stellarcyber.ai/
js.navattic.com
Read at https://stellarcyber.ai/
alb.reddit.com, pixel-config.reddit.com
Read at https://stellarcyber.ai/
www.redditstatic.com
Read at https://stellarcyber.ai/
ibc-flow.techtarget.com, trk.techtarget.com
Read at https://stellarcyber.ai/
js.usemessages.com
Read at https://stellarcyber.ai/
js.zi-scripts.com
Read at https://stellarcyber.ai/
Checked 1 address on 2026-10-14.
Show the 1 address we checked
https://stellarcyber.ai/ – third-party requests before any interaction: 828-dzv-249.mktoresp.com, ad.doubleclick.net, alb.reddit.com, api.hubspot.com, arttrk.com, bat.bing.com, bat.bing.net, cdn.bizible.com, cdn.bizibly.com, ibc-flow.techtarget.com, js.hs-analytics.net, js.hs-banner.com, js.navattic.com, js.usemessages.com, js.zi-scripts.com, munchkin.marketo.net, o.clarity.ms, pixel-config.reddit.com, px.ads.linkedin.com, region1.analytics.google.com, scripts.clarity.ms, snap.licdn.com, stats.g.doubleclick.net, track.hubspot.com, trk.techtarget.com, www.clarity.ms, www.google.com, www.google.de, www.googletagmanager.com, www.redditstatic.com
Is this wrong? Send us the URL
Across the market: No third-party tracking before consent in SIEM and security operations: 1 of 41 companies
✗
Certifications named (SOC 2, ISO 27001)
weight 1 of 3
No named certification found.
Checked 6 addresses on 2026-10-14.
Show the 6 addresses we checked
https://stellarcyber.ai/security – Not the expected content type but "image/svg+xml".https://stellarcyber.ai/trust – reached, no match (HTTP 200)https://stellarcyber.ai/trust-center – reached, no match (HTTP 200)https://stellarcyber.ai/compliance – reached, no match (HTTP 200)https://stellarcyber.ai/legal/security – reached, no match (HTTP 200)https://trust.stellarcyber.ai/ – The name "trust.stellarcyber.ai" could not be resolved.
Is this wrong? Send us the URL
Across the market: Certifications named in SIEM and security operations: 19 of 40 companies
✗weight 1 of 3
No named privacy contact found.
Checked 7 addresses on 2026-10-14.
Show the 7 addresses we checked
https://stellarcyber.ai/legal/privacy – reached, no match (HTTP 200)https://stellarcyber.ai/privacy – reached, no match (HTTP 200)https://stellarcyber.ai/privacy-policy – reached, no match (HTTP 200)https://stellarcyber.ai/legal/privacy-policy – reached, no match (HTTP 200)https://stellarcyber.ai/legal/privacy-notice – reached, no match (HTTP 200)https://stellarcyber.ai/trust/privacy – reached, no match (HTTP 200)https://stellarcyber.ai/datenschutz – reached, no match (HTTP 200)
Is this wrong? Send us the URL
Across the market: Named privacy contact in SIEM and security operations: 19 of 39 companies